Published on 4/30/2026 by Daniel SCHNETZER
Last updated : 11/3/2026
Introduction
Ransomware attacks pose a major threat to businesses. By encrypting files and blocking access to IT systems, cybercriminals can cause business disruption, data loss and significant financial consequences.
In response to these risks, having IT backups is not enough: companies must also ensure that their backups are reliable, secure and capable of restoring data within an acceptable timeframe. Backups that have never been tested may prove unusable when the business needs them most.
How can you verify the effectiveness of your backups before a cyberattack? Which tests should you perform, and what best practices can help strengthen your IT infrastructure’s cyber resilience?
Why Should You Test Your Backups Against Ransomware?
Data backups are an essential part of a cybersecurity strategy. However, some attacks also target backup systems to prevent data recovery after files have been encrypted.
To reduce these risks, businesses must regularly verify the integrity of their backup copies, their accessibility and their ability to restore IT environments.
The risks of untested backups
A backup may appear to be working correctly without actually being usable. Corrupted files, incomplete copies, configuration errors or compromised credentials can prevent an effective restoration.
The main risks include:
- Data loss: some information may be missing or corrupted.
- Prolonged downtime: an unexpectedly complex restoration process can delay business recovery.
- Backup compromise: an attacker may delete or encrypt copies that are accessible through the network.
- Incomplete recovery: applications may restart without the dependencies, configurations or databases they need to function properly.
How can you verify backup reliability?
An effective strategy relies on several complementary checks: verifying that backup jobs complete successfully, checking data integrity and performing restoration tests in an isolated environment.
It is also recommended to verify that backups remain accessible if the usual administrative accounts are compromised.
The objective is to confirm that the business can recover its data and essential services, even if its primary infrastructure is affected by ransomware.
How Can You Test the Effectiveness of Your Backups in Practice?
To assess the reliability of a backup system, it is not enough to monitor automated reports. Tests must demonstrate that data can actually be restored and that recovered systems function correctly.
Perform regular restoration tests
The first step is to select files, databases and applications that represent the company’s operations, then restore them in a test environment.
These operations help verify:
- The integrity of restored data, by comparing recovered files with the expected data.
- Application consistency, particularly for databases and business-critical systems.
- Restoration times, to measure how long recovery actually takes.
- Backup availability, including when production systems are inaccessible.
Tests should cover several types of data and be repeated at regular intervals. A successful restoration of a single file does not guarantee that an entire IT system can be recovered.
Simulate a ransomware scenario safely
A business can conduct a recovery exercise without triggering encryption on its production systems.
The scenario involves isolating a test environment, selecting a backup point from before the simulated incident, and restoring the data and services required for recovery.
This simulation helps assess the IT team’s ability to identify clean backup copies, follow restoration procedures and verify that recovered systems show no signs of compromise.
It is essential to never test real ransomware on a production environment. Exercises must be controlled, documented and carried out under safe conditions.
Measure RTO and RPO objectives
Two indicators help assess recovery capabilities:
- RTO (Recovery Time Objective): the maximum acceptable time required to restore a service after an outage.
- RPO (Recovery Point Objective): the maximum amount of data the business can afford to lose, expressed as a period of time.
For example, an RPO of four hours means the business aims to limit data loss to the equivalent of four hours of activity. An RTO of eight hours means the service must be restored within that timeframe.
Restoration tests make it possible to compare these objectives with actual results and identify necessary improvements.
How Can You Strengthen Backup Protection Against Ransomware?
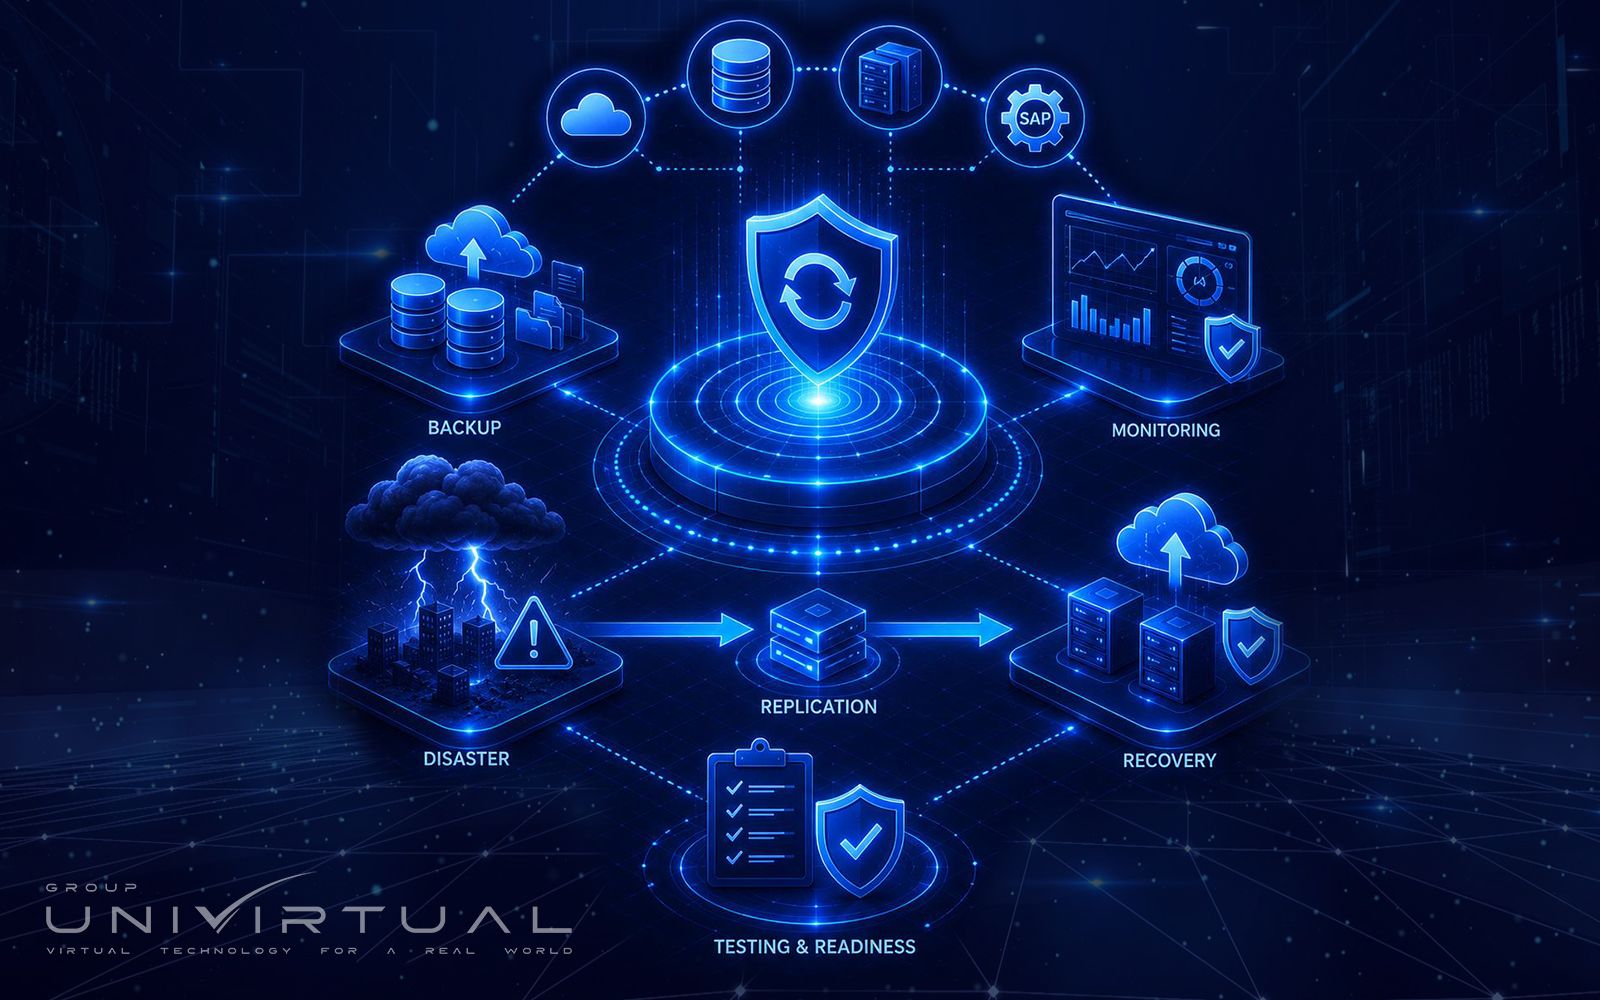
Testing backups is essential, but protection also depends on an appropriate architecture, controlled access and clearly defined recovery procedures.
Adopt a resilient backup strategy
The 3-2-1 backup rule provides a useful foundation: keep three copies of your data, on two different types of storage media, with one copy stored off-site.
To improve ransomware resilience, this approach can be strengthened with offline backups, isolated from the network, or immutable backups, which cannot be modified or deleted during a defined retention period.
These mechanisms reduce the risk of an attacker compromising production data and backup copies simultaneously.
Secure access and monitor backups
Backup systems must be protected as critical components of the IT infrastructure. Recommended measures include:
- Strict access management, using dedicated accounts and limited privileges.
- Multi-factor authentication (MFA), where supported by the solution.
- Environment separation, to limit the spread of an attack from production systems.
- Backup job monitoring, to detect failures, unusual deletions or suspicious changes.
- Documented restoration procedures, accessible even if the usual tools are unavailable.
The frequency of testing should be adapted to application criticality, business requirements and the risks facing the organisation.
Integrate testing into a disaster recovery plan
Test results should feed into the IT disaster recovery plan (DRP) and, more broadly, the business continuity framework.
It is useful to document the data restored, the time taken, any errors encountered and the corrective actions required. Regular exercises also help prepare teams to make the right decisions during a crisis.
For businesses looking to strengthen their infrastructure, specialist support in cloud computing, IT security and business continuity can help define a strategy suited to their needs.
Conclusion
To deal with ransomware, it is essential to regularly test your backups, verify data integrity and master RTO and RPO objectives. These best practices help to strengthen cyber resilience and ensure faster business recovery after a cyberattack.
Trust UNIVIRTUAL to secure your backups and strengthen your IT infrastructure. Discover our solutions or contact our teams for a free initial evaluation.