Published on 2/18/2026 by Daniel SCHNETZER
Last updated : 11/3/2026
Introduction : NIS2, a Cybersecurity Challenge for SMEs
With cyberattacks on the rise, the NIS2 Directive strengthens cybersecurity requirements across Europe. Its aim is to improve the protection of information systems, risk management and business continuity.
In 2026, SMEs must determine whether they fall within its scope and anticipate the measures needed to achieve NIS2 compliance. Beyond regulatory obligations, the key challenge is to protect data, minimize disruptions and strengthen digital resilience.
NIS2 : Which Companies Are Affected?
The NIS2 Directive covers several sectors, including energy, healthcare, transport, manufacturing and digital infrastructure.
Its application depends on the sector, the size of the company and certain specific provisions. Some organizations may also be covered regardless of their size.
SMEs must therefore assess their situation against European criteria and applicable national rules. Even when they are not directly subject to NIS2, they may have to meet cybersecurity requirements imposed by their customers or partners.
What Are the Main NIS2 Obligations?
Organizations within the scope of the directive must implement a structured cybersecurity approach tailored to the risks they face.
The main measures include :
- Risk management: identify vulnerabilities and define appropriate protective measures.
- System security: strengthen access controls, apply updates and protect data.
- Supplier security: assess risks associated with service providers and the supply chain.
- Incident management: establish detection, response and notification procedures.
- Business continuity: prepare to restore services following an outage or cyberattack.
Cybersecurity is therefore becoming a governance issue involving management, IT teams and service providers.
How Can SMEs Prepare for NIS2 Compliance in 2026?
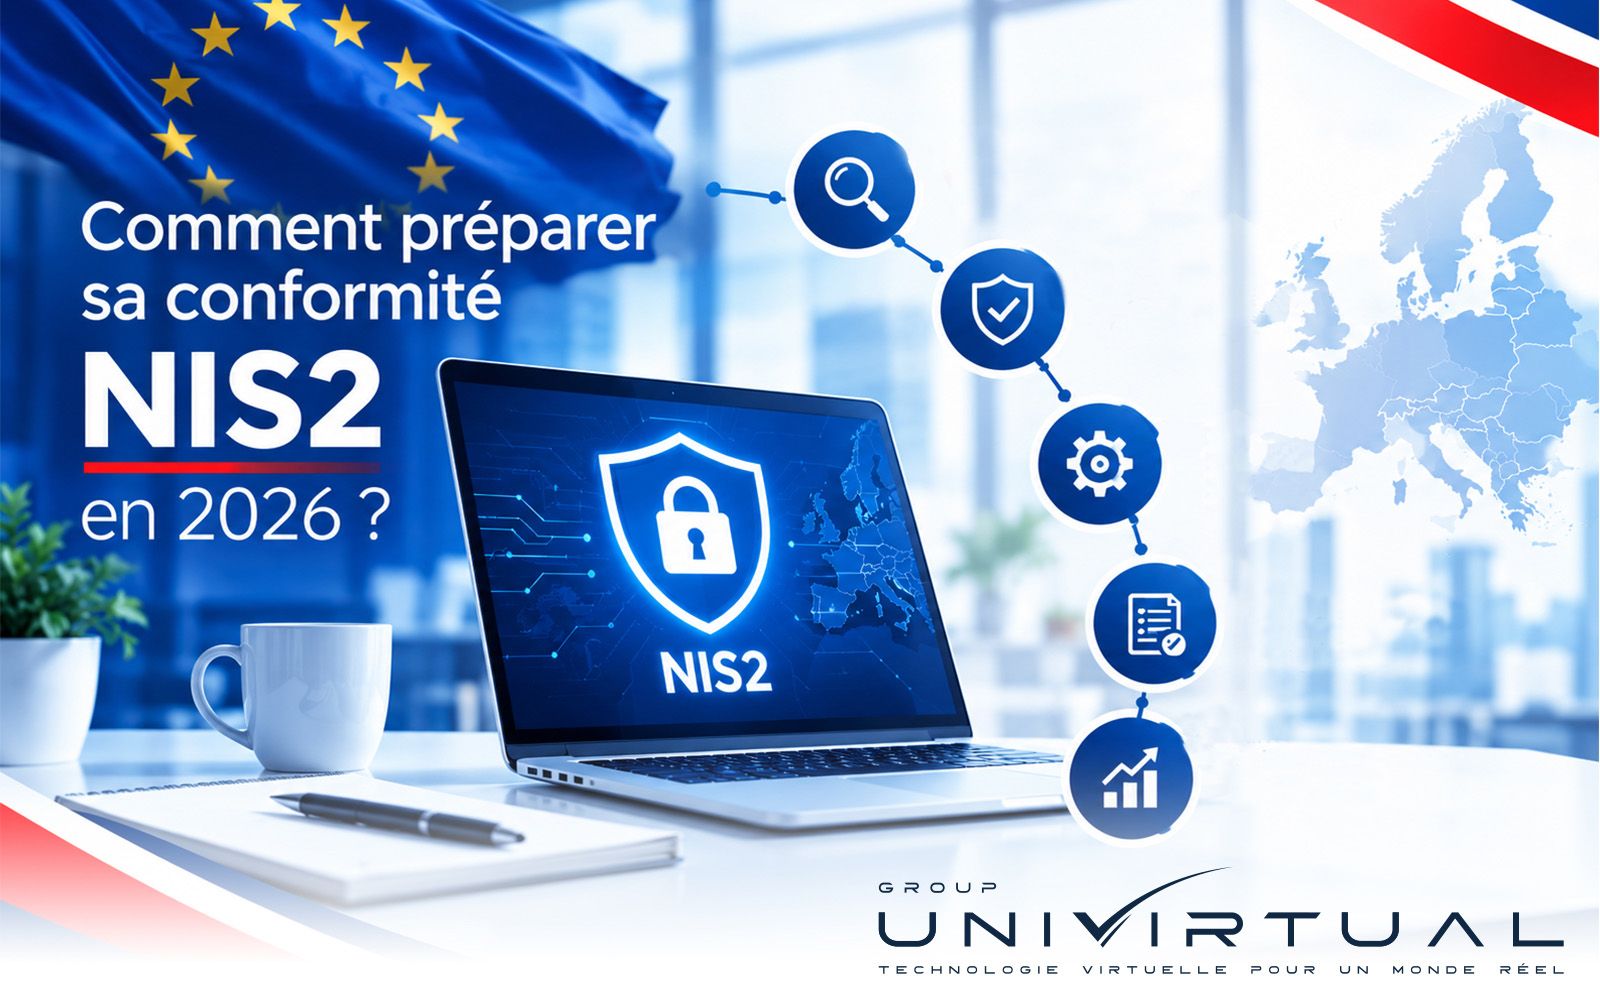
To anticipate NIS2 requirements, SMEs can follow five steps :
- Assess their regulatory status and determine whether they fall within the scope of the directive.
- Conduct a cybersecurity assessment to identify risks and vulnerabilities.
- Prioritize actions: secure access, apply updates, monitor systems and protect backups.
- Prepare for crisis management through documented procedures and recovery tests.
- Monitor implemented measures and regularly update security policies.
This approach helps build an action plan proportionate to the company’s risks and resources. It also makes it easier to allocate responsibilities and track improvements over time.
NIS2 and Management Accountability : A Governance Challenge
The NIS2 Directive strengthens the role of company leaders in overseeing cybersecurity. IT security can no longer be considered solely a technical responsibility: it must be integrated into the company’s strategic decisions.
Management must ensure that risk management measures are appropriate, that teams have the necessary resources and that employees are aware of cyber threats. For SMEs, this approach helps anticipate incidents and establish a consistent security policy.
Backup and Business Recovery : Limiting the Impact of Cyberattacks
A ransomware attack or IT outage can disrupt a company’s operations for an extended period. To limit these consequences, it is essential to maintain secure backups that are regularly tested and protected against unauthorized access.
An IT disaster recovery plan (DRP) defines the procedures required to restore critical systems and minimize downtime. Combined with resilient infrastructure and regular testing, these measures help strengthen service continuity and address the cybersecurity challenges associated with NIS2.
Cloud and Cybersecurity : A Driver of Resilience
A well-designed cloud infrastructure can facilitate data protection, system monitoring and recovery after an incident. However, the cloud does not automatically guarantee NIS2 compliance.
When choosing a provider, companies should consider several criteria: data location, access management, backup security, service availability and incident management procedures.
Digital sovereignty and transparency regarding hosting arrangements are also important for managing risks associated with data and infrastructure. Companies must understand where their data is hosted, who can access it and how it can be recovered in the event of an incident.
Conclusion : Anticipating NIS2 to Strengthen SME Security
In 2026, the NIS2 Directive encourages affected companies to strengthen their governance, IT security and ability to manage incidents.
For SMEs, the priority is to verify their obligations, identify vulnerabilities and implement measures suited to their risks. Infrastructure security, data protection and disaster recovery planning should be treated as components of a single strategy.
UNIVIRTUAL supports organizations in their efforts to address cloud computing, cybersecurity and digital infrastructure resilience, with data centers in France and Switzerland.
Explore UNIVIRTUAL’s cloud solutions to learn more about infrastructure hosting and security.
The goal is to make cybersecurity a driver of resilience and trust rather than simply a response to regulatory requirements.