Published on 7/16/2026 by Daniel SCHNETZER
Last updated : 7/16/2026
Introduction : Cloud Computing as a Digital Sovereignty Issue
Cloud computing has become a cornerstone of businesses’ digital transformation. Business application hosting, sensitive data storage, production environments and collaboration tools now rely on digital infrastructures often distributed across several countries.
However, this dependence raises a strategic question : who actually controls the infrastructures on which a company’s operations depend ?
International tensions, regulatory developments, economic sanctions and the concentration of the technology market can change the conditions under which certain digital services are accessed. An infrastructure that is technically efficient and secure is therefore not necessarily free from geopolitical risks.
For executive management, CIOs, CTOs and CISOs, geopolitical risk in the cloud must now be incorporated into digital risk management. The challenge is not simply to determine where data is stored, but also to understand who operates the infrastructure, which laws may apply and what alternatives remain available in the event of a crisis.
Geopolitical Risk in the Cloud : What Does It Mean ?
Geopolitical risk in the cloud refers to all threats arising from international relations, political decisions and economic power dynamics that may affect access to digital infrastructure, data or a company’s IT services.
Unlike a conventional cyberattack, this risk does not necessarily originate from a malicious actor directly targeting an organisation. It may result from a government decision, a trade restriction, an international conflict or a change in the legal framework applicable to a provider.
Several situations deserve particular attention :
- Restrictions on access to technology, which may limit the availability of certain software, components or services.
- Extraterritorial legislation, which may subject certain providers to foreign legal obligations, depending on their legal circumstances.
- Supply chain tensions, which may affect equipment, updates and maintenance.
- Technological dependencies, which make a company vulnerable when it has no operational alternative.
These risks may result in service disruptions, difficulties recovering data, increased costs or a loss of control over critical digital assets.
For business leaders, the question is therefore as much strategic as it is technical: can the company continue operating if its cloud provider becomes inaccessible or if the terms governing its services change abruptly ?
Data Location and Jurisdiction : Two Different Issues
Hosting data in a European data centre is an important element in managing risk, but it is not always sufficient to guarantee full digital sovereignty.
It is essential to distinguish between data location and the jurisdiction applicable to the provider.
Data location refers to the country in which data is stored or processed. Jurisdiction depends, in particular, on the contracting entity, the corporate structure of the group, its activities and the laws that may apply to it.
For example, the US CLOUD Act provides, subject to certain legal conditions, for data disclosure obligations for providers subject to US jurisdiction, including where the relevant data is stored abroad. Its application nevertheless depends on the circumstances and the applicable jurisdictional criteria.
This does not mean that a foreign government has automatic access to all data hosted by an international provider. However, European data storage alone does not eliminate all exposure to extraterritorial legal requirements.
To assess the actual level of cloud sovereignty, companies should therefore examine several criteria: the identity of the contracting entity, ownership and corporate control, administrative access, subcontractors, applicable jurisdictions and contractual safeguards.
This analysis makes it possible to move beyond an approach focused solely on the physical location of servers.
Dependence on a Cloud Provider : A Strategic Risk for Businesses
Concentrating IT services with a single provider can simplify day-to-day operations, but it also creates a dependency that may become critical.
This situation, commonly referred to as vendor lock-in, occurs when a company’s applications, data and processes become heavily dependent on a provider’s proprietary technologies.
In the event of a significant price increase, a regulatory restriction or a prolonged outage, migrating to another environment may prove complex, costly and time-consuming.
The risk increases when several essential components depend on the same provider: hosting, backups, identity management, security tools and monitoring.
To reduce this exposure, companies can implement a cloud exit and reversibility strategy based on several principles:
- Document technical dependencies between applications, data and services.
- Ensure data portability and verify the available export formats.
- Regularly test migration and restoration procedures.
- Assess alternative solutions for the most critical services.
- Establish contractual provisions covering reversibility, data return deadlines and exit conditions.
A multicloud or hybrid architecture can also help diversify dependencies. However, it does not automatically guarantee greater resilience: it involves additional complexity, costs and skills requirements.
The objective is therefore not to systematically multiply providers, but to preserve a genuine ability to make decisions and maintain operational continuity.
Digital Sovereignty : What Criteria Should Guide Your Cloud Choice ?
Digital sovereignty cannot be reduced to a provider’s nationality. It depends on an organisation’s ability to control its data, access, technologies and operational choices.
For European businesses, an infrastructure hosted in France or Switzerland can help strengthen this control, provided that legal and operational aspects are also assessed.
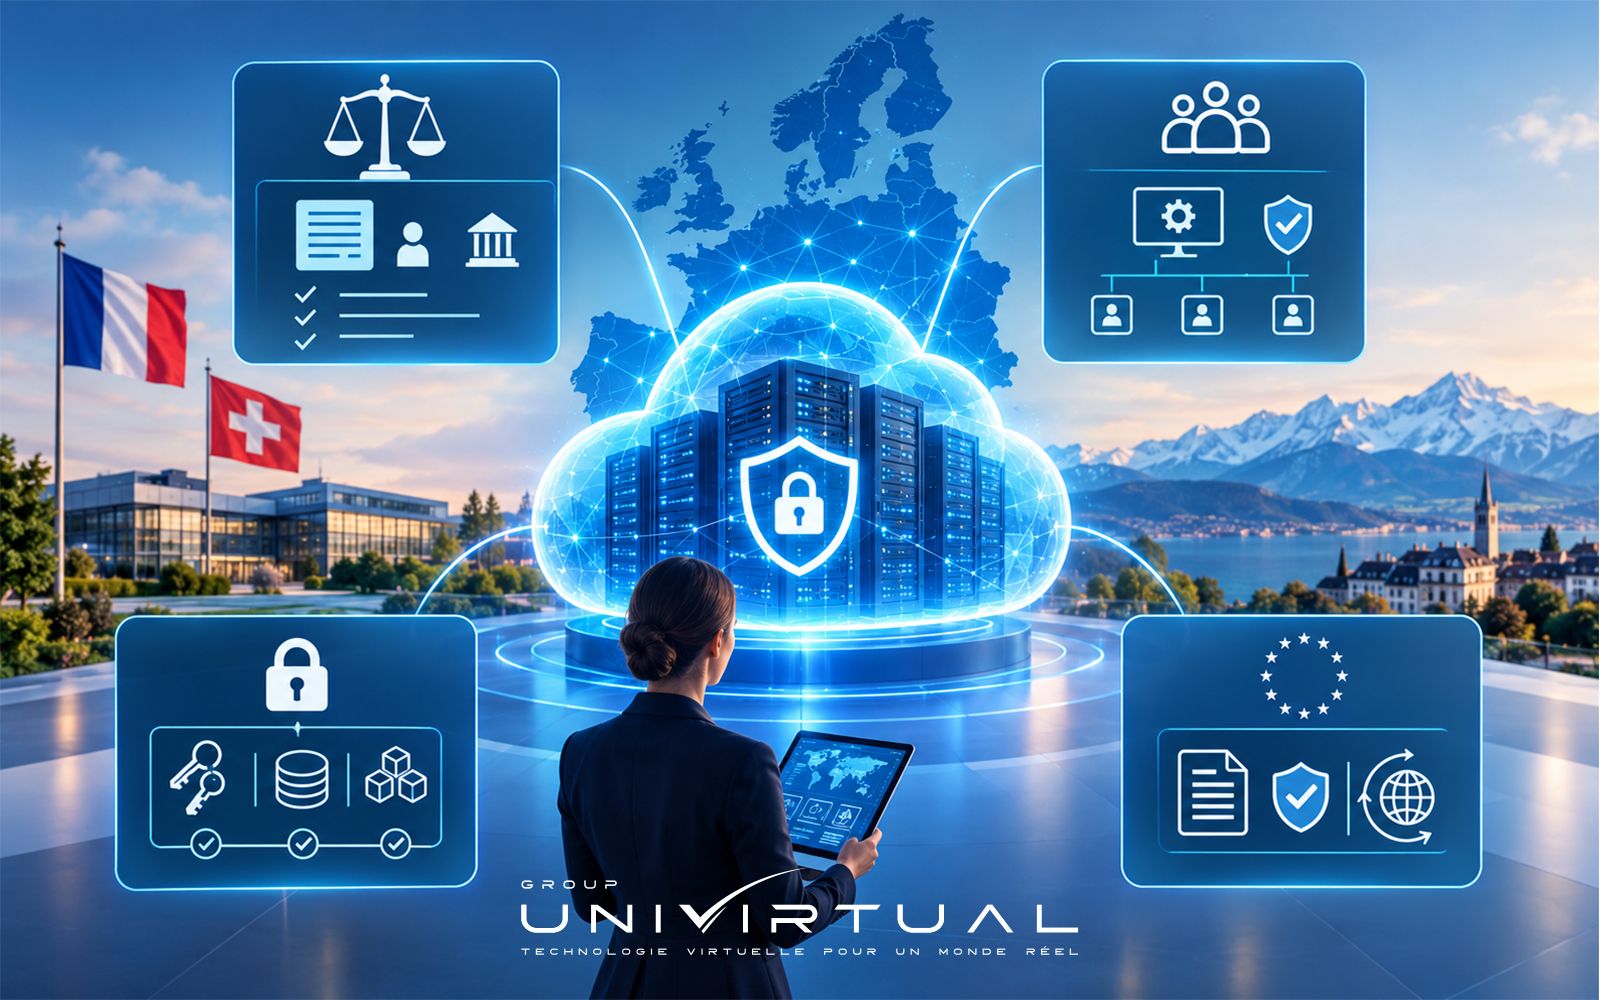
A thorough evaluation should cover four main areas.
1. Legal Sovereignty
Companies should identify the entity providing the service, the laws that may apply to it and the circumstances under which authorities may request access to data.
2. Operational Control
Companies need to know which individuals and organisations may administer their infrastructure, how access controls are implemented and how operations are monitored.
3. Data Protection
Encryption, key management, environment segmentation and access logging all help reduce risk. Encryption is particularly important when the company retains effective control over its encryption keys.
4. Regulatory Compliance
The GDPR governs transfers of personal data outside the European Economic Area. Depending on the circumstances, an adequacy decision or appropriate safeguards, such as standard contractual clauses, may be required. Compliance with these mechanisms must be assessed in light of the actual circumstances of the transfer.
Sovereignty should therefore be viewed as a set of verifiable safeguards rather than a simple marketing promise.
How Can Geopolitical Risk Be Incorporated into a Cloud Strategy ?
Managing geopolitical risk requires a structured approach involving executive management, the CIO, the CISO, legal teams and business stakeholders.
The first step is to map critical digital assets : sensitive data, essential applications, providers, subcontractors and technological dependencies.
The next step is to assess the consequences of an outage or access restriction. Can an application be replaced? Can data be recovered independently of the provider? How long can the business continue operating without the service in question ?
This analysis should be complemented by a business continuity and disaster recovery plan, isolated backups and regular restoration tests.
Companies can also establish selection criteria covering legal transparency, reversibility, infrastructure location and diversification of dependencies.
Finally, geopolitical risk must be monitored continuously. Changes in regulations, contracts, supply chains and international relations may require periodic reassessment of technology choices.
Why Does European Infrastructure Matter ?
Choosing a provider with infrastructure in Europe can make it easier to control data location, communicate with operations teams and understand contractual commitments.
However, a European cloud is not automatically a sovereign cloud. The provider’s legal structure, potential technological dependencies and administrative practices must also be considered.
Companies should therefore seek a coherent combination of controlled hosting, technical security, transparency and the ability to exit or migrate.
This approach makes it possible to build an infrastructure aligned with the organisation’s actual needs without confusing sovereignty, regulatory compliance and IT security: these three dimensions complement one another, but they remain distinct.
Conclusion : Cloud Control Is Becoming a Governance Issue
Geopolitical risk in the cloud encourages companies to move beyond a vision focused solely on technical performance and hosting costs. The real question is whether they can retain control over their data and ensure operational continuity in an uncertain international environment.
Understanding applicable jurisdictions, limiting critical dependencies, planning for reversibility and strengthening resilience are now essential elements of digital governance.
In this context, UNIVIRTUAL supports organisations with cloud solutions and digital infrastructure based on data centres in France and Switzerland, following an approach focused on security, performance and resilience.
To explore this approach further, discover UNIVIRTUAL’s cloud solutions, digital infrastructure and professional cloud offering.
The objective is not to eliminate all risk, but to build a digital environment in which dependencies are understood, safeguards are verifiable and alternatives are operationally viable.