Published on 8/28/2026 by Clémence LUCIANI
Last updated : 11/3/2026
Digital Dependencies as a Strategic Business Issue
Businesses increasingly rely on complex digital ecosystems comprising cloud infrastructure, business applications, IT service providers, software vendors and outsourced services. This interconnected environment supports agility and performance, but it also creates new vulnerabilities.
A company may have robust internal security measures and still be exposed to a vulnerability affecting its hosting provider, software publisher or IT service partner. Cybersecurity no longer depends solely on an organisation’s own protective measures, but also on the security practices of its partners.
This issue is highlighted by the European Union Agency for Cybersecurity (ENISA) in its analysis of the cyber threat landscape. Its work underlines how digital dependencies can expand the attack surface and amplify the consequences of a security incident.
For CEOs, CIOs, CTOs and cybersecurity leaders, the challenge is clear : strengthening corporate cyber resilience means managing risks across the entire digital supply chain.
Analysing the Threat : When IT Suppliers Become an Entry Point for Cyberattacks
An Attack Surface That Extends Beyond the Company
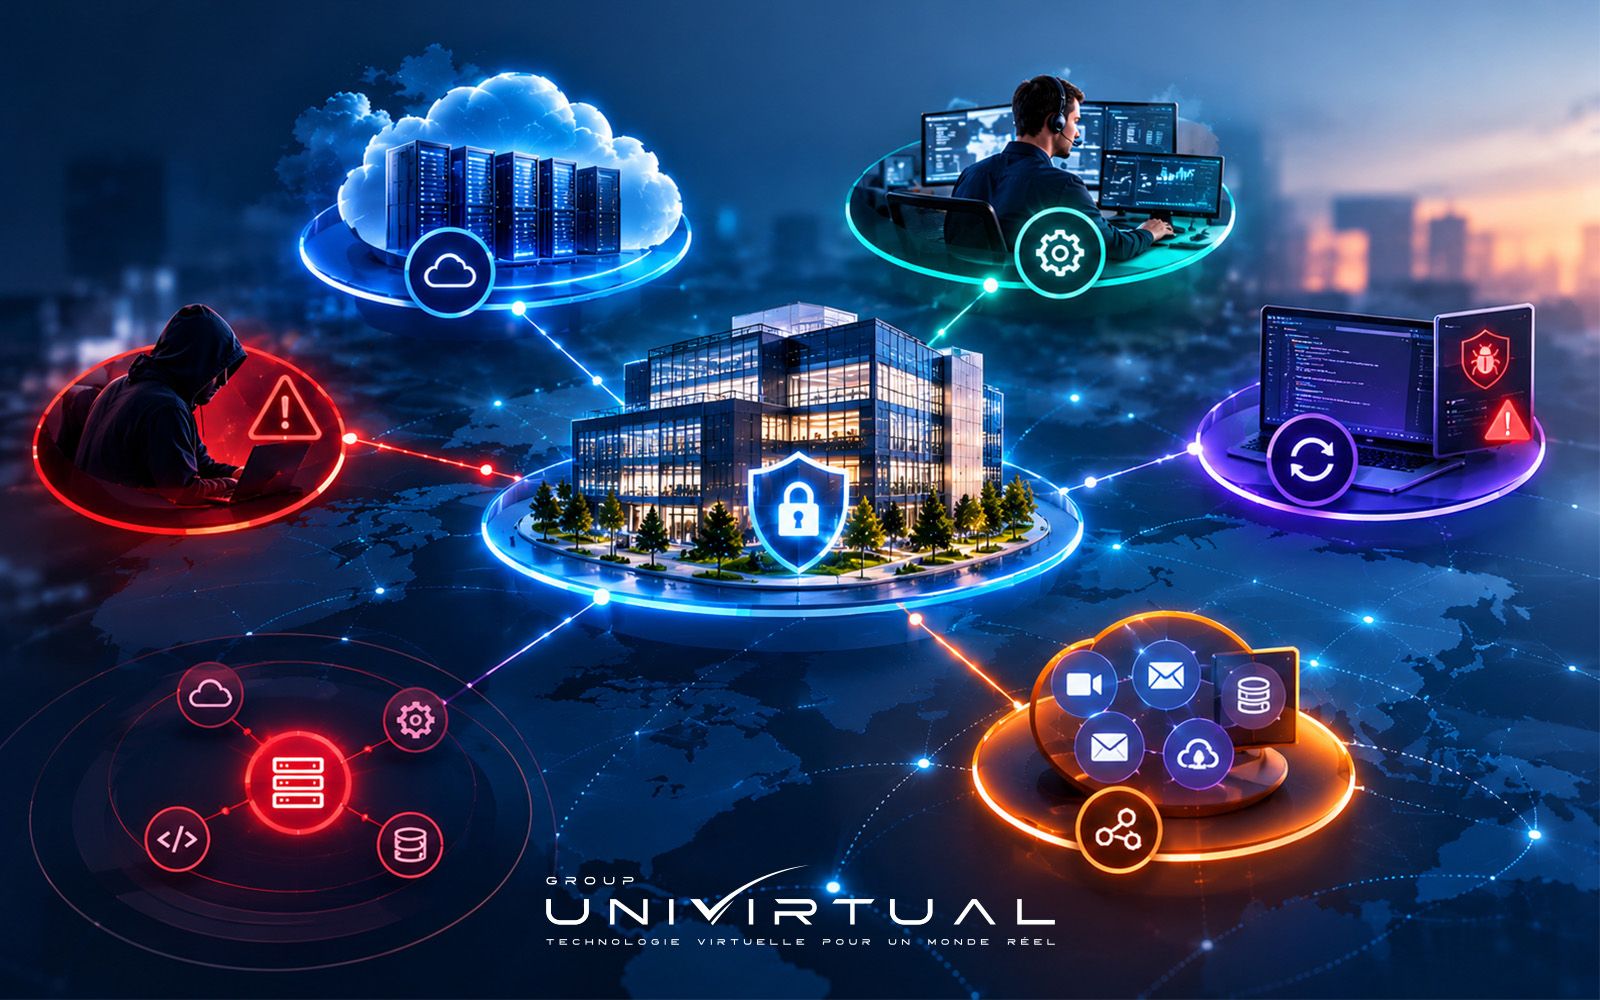
Information systems are increasingly interconnected. An IT service provider may have privileged access to several customer environments, while a widely used software product can become a large-scale attack vector.
Cybercriminals exploit these connections by targeting not only end-user organisations, but also their suppliers, tools and infrastructure. A compromise affecting one partner can provide attackers with a way around certain security controls and potentially affect multiple organisations.
Attacks targeting digital supply chains and third-party service providers are particularly concerning because their effects can spread far beyond the organisation initially compromised.
The risk is no longer limited to direct attacks : it can be indirect, shared and systemic.
Cloud, Software and Managed IT Services : Dependencies That Must Be Mapped
Digital dependencies take several forms :
- Cloud providers, which host applications, data and critical infrastructure
- IT and managed service providers, which administer systems and may hold extensive access privileges
- Software vendors, whose updates or vulnerabilities can affect many customers
- Third-party services, including backup, authentication, monitoring and communication tools
Problems arise when these dependencies are poorly identified or inadequately controlled. An organisation, for example, may rely on a single provider for hosting, backup and system administration.
This concentration can create a single point of failure: a security breach, major outage or service disruption may affect several essential business functions at once.
The priority is therefore to identify dependencies, assess their criticality and understand the operational consequences of a supplier failure.
Business Implications : Moving from Internal Security to End-to-End Resilience
1. Assessing IT Supplier Risks
Third-party risk management should go beyond signing a contract or completing a compliance questionnaire. It must provide a practical assessment of a supplier’s security posture, incident management procedures and ability to maintain services.
Businesses should assess :
- Authentication mechanisms and access controls
- Vulnerability management and software patching procedures
- Backup systems and disaster recovery capabilities
- Service availability commitments and incident notification requirements
- Data recovery arrangements and supplier exit provisions
A strategic supplier should be assessed according to the business risk it creates, not just its cost or technical performance.
2. Strengthening Access Governance and Supplier Management
Access granted to external partners is a major security concern. Poorly protected administrator accounts, shared credentials and permissions that remain active after a project ends can facilitate unauthorised access.
An effective strategy relies on the principle of least privilege, multifactor authentication (MFA), activity logging and regular access reviews.
Access should be limited to the resources required, granted for an appropriate period and revoked as soon as it is no longer justified.
Businesses should also clearly define responsibilities between internal teams and external providers, particularly for monitoring, alert handling and incident response.
3. Preparing for Business Disruption Caused by a Supplier Failure
Cybersecurity is not only about preventing attacks. It must also enable organisations to maintain or restore essential operations when an incident occurs.
A cyber resilience strategy should include scenarios involving suppliers: cloud service outages, compromised administration tools, loss of access to a platform or disruption affecting a critical service provider.
Key measures include :
- Independent backups that are regularly tested
- Recovery objectives based on the criticality of each service
- Procedures for operating in degraded mode
- Business continuity and disaster recovery plans
- Alternative providers or clearly defined exit strategies
The objective is to reduce operational dependence on a single supplier and establish realistic recovery capabilities.
Cloud and Cybersecurity : Building a Controlled Digital Ecosystem
Cloud computing gives businesses scalable resources, greater flexibility and opportunities for redundancy. However, moving to the cloud does not eliminate risk: it changes how responsibility is distributed between the company and its providers.
Responsibilities for securing identities, configurations, data and usage must be clearly defined. Businesses should also understand their provider’s security controls, restoration capabilities and contractual commitments.
Diversifying providers can reduce certain concentration risks, but diversification must be carefully planned. Multiple environments without consistent governance can increase complexity and introduce new vulnerabilities.
Businesses should favour a coherent architecture built around visibility, segmentation, monitoring and recovery capabilities. Data location, administrative access conditions and portability also deserve particular attention.
Cyber resilience must therefore be a core cloud architecture principle, not a measure introduced after an incident.
Why Choose UNIVIRTUAL to Secure Your Digital Infrastructure ?
Managing digital dependencies requires an approach that combines infrastructure, security and business continuity.
UNIVIRTUAL supports organisations in building professional cloud environments tailored to their performance and protection requirements. Depending on each company’s needs, this approach may include :
- Cloud infrastructure designed for business environments
- Backup and data recovery solutions
- An approach focused on service availability
- Support for data security and access management
- Guidance tailored to business continuity requirements
The objective is to help organisations gain greater control over their digital environments and strengthen their ability to withstand incidents.
Discover UNIVIRTUAL’s cloud solutions and cybersecurity services to build an infrastructure aligned with your operational and strategic priorities.
Strategic Conclusion : Cyber Resilience Depends on the Entire Digital Ecosystem
Digital dependencies are unavoidable, but they should never remain blind spots in a company’s security strategy.
The issues highlighted by ENISA demonstrate how cyber threats can spread through suppliers and interconnected infrastructure. Business leaders must therefore extend risk management beyond their internal perimeter: map critical dependencies, control access, assess suppliers and test recovery capabilities.
A resilient business is not simply one that can prevent an attack. It is an organisation that understands its critical dependencies, limits the impact of an incident and maintains operations even when a partner fails.
From this perspective, cloud computing and cybersecurity must be designed together as part of a sustainable, controlled and resilient digital strategy.